
One entropy pool for the whole data centre.
An appliance in your own racks that gives every HSM, server and service on the site verified quantum entropy. Nothing in the applications changes, and the entropy is monitored the whole time it is in use.
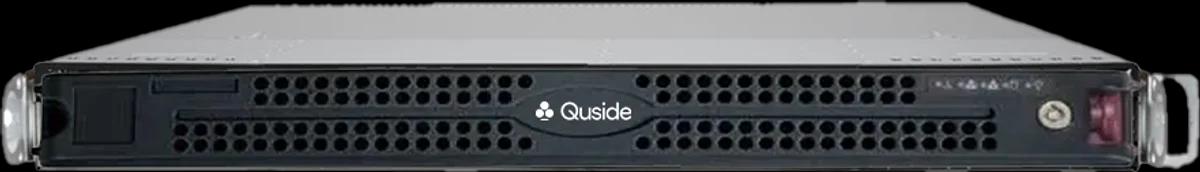
A 19-inch rack appliance in your own data centre, or the same pool as a virtual appliance.
Standard HTTP clients on your private network, and the QRNG Open API developed with Palo Alto Networks.
Entropy quality recorded per appliance and per site, and exported to the Prometheus monitoring you already run.
What is a virtual entropy pool?
A virtual entropy pool is one source of high-quality randomness that every system on a site can draw from. Instead of each server, HSM and appliance relying on whatever randomness its own hardware happens to produce, they all take it from one place that is designed, measured and audited for the job.
Entropy Core is that place. The appliance generates quantum entropy, checks it while it runs, and answers requests from systems on your private network through a REST API, using standard HTTP clients. It supports the QRNG Open API, the interface Quside developed with Palo Alto Networks.
Because the quality of the entropy is recorded per appliance and per site, the pool also produces evidence: a record an auditor can read of where your keys’ randomness came from, and that it was healthy when they were made.
When Entropy Core is the right choice.
It fits when many systems on one site generate keys, some of them have no slot for a card, and you need one record of the randomness behind all of them.
Architectures
- Data centres where many servers, HSMs and services generate keys, and each relies on its own randomness today.
- Hosts with no free slot for a card, and the virtual machines and containers running on them.
- Sites that have to show auditors where their keys’ randomness came from, under DORA or NIS2.
- Multi-tenant halls where each zone should draw entropy locally, with nothing installed on the hosts.
Who usually specifies it
- Infrastructure and security architects responsible for key generation across a site.
- HSM, PKI and key-management owners who need a source they can name in an audit.
- Compliance and risk teams preparing DORA or NIS2 evidence on cryptography.
- Platform teams running servers, virtual machines and containers at scale.
If one server needs entropy inside its own chassis, the Garnet™ PCIe card is the shorter route. Entropy Core serves the rest of the site.
Specifications.
The engine, the request rate and the payload limits are in the datasheet, which an engineer sends with the figures that apply to your site.
| Form factor | 1U 19″ rack appliance, or a virtual appliance |
|---|---|
| Where it sits | In your own data centre, on your private network |
| Deployment | One pool per site, sized with you |
| Interface | REST HTTP API, for standard HTTP clients |
| Open interface | QRNG Open API, developed with Palo Alto Networks |
| Host software | None required on the consuming hosts |
| Monitoring | Entropy quality per appliance and per site, exported to Prometheus |
| Lifecycle status | One-site pilots |
| Entropy engine, request rate and payload limits | Available on request — ask an engineer Ask for the datasheet figures that apply to your site and your consumers. |
Every key-maker on the site, connected.
A Garnet card goes inside one server. Entropy Core serves the rest: the systems with no free slot, and the ones you cannot open.
HSMs
Payment, PKI and key-management HSMs seeded from one verified source on the site.
Servers and virtual machines
Hosts without a free slot for a card, and the virtual machines running on them.
Containers and services
Containerised services draw entropy through a standard HTTP client. No agent to install.
Gateways
VPN gateways, and the OT gateways in a control centre, that need keys they can trust.
Key quality you can show an auditor.
Banks working to DORA and operators of critical infrastructure working to NIS2 have to show how their cryptography is governed, and randomness is where every key starts. Entropy Core records entropy quality per appliance and per site, and exposes it to the monitoring you already run through Prometheus.
Entropy Core carries no certificate of its own. NIST SP 800-90B certificate E178 and the ENS Alta qualification are scoped to Quside PCIe One and FMC One, and do not extend to the appliance.
What the engineering work looks like.
The consuming hosts need nothing installed. The work is placing the appliances, pointing consumers at them and wiring the monitoring into your own.
Interfaces
A REST HTTP API on your private network, which any standard HTTP client can call, and the QRNG Open API for applications already written against it.
On the consuming hosts
Nothing to install. Servers, virtual machines and containers request entropy over the network inside your own site; no agent runs on them.
Monitoring
Entropy quality is recorded per appliance and per site and exported to Prometheus, so it lands in the dashboards and alerts you already run.
Expected effort
Racking an appliance and pointing a first consumer at it is a short task. Sizing the pool across the site and deciding which systems move first is the part worth a workshop.
Where one pool changes the design.
Sites where many systems make keys and someone has to account for all of them.
Banks working to DORA
One pool per data centre seeds the payment, PKI and key-management HSMs and the servers around them, and the monitoring record gives the evidence of key quality an audit asks for.
Critical infrastructure working to NIS2
An appliance at each site feeds control-centre servers, OT gateways and HSMs, so entropy is produced inside each operator’s own network and its quality is recorded where the audit will look.
Multi-tenant and AI data halls
Each tenant zone draws entropy from appliances in its own hall, with no agents on the hosts and nothing added to the compute nodes.
Getting ready for post-quantum re-keying
Moving to post-quantum algorithms re-keys everything. Starting that from one measured source on the site means every new key begins with entropy you can account for.
Start with one site.
- 01
Assess
Map where keys are generated on the site — HSMs, servers, services — with our engineers.
- 02
Pilot
One Entropy Core on one site or cluster, with monitoring on from the first day.
- 03
Scale
Size appliances per site and extend the pool through the QRNG Open API.
What to ask for.
Every document has a name on it. Say which one you need and an engineer sends it.
Entropy Core datasheet
On requestThe engine, request rate, payload limits and appliance detail a design review needs, issued directly to your team.
How runtime observability works
PublishedWhat is measured while the source runs, what the health state means, and what the record lets an auditor check.
Sizing and pilot plan
With the pilotWhere the appliances go on your site, how consumers connect, and what the monitoring will show from the first day.
Put one on one site.
Point your own consumers at it and read the monitoring yourself. Tell us which HSMs, servers and services generate keys on the site when you ask.